Friday, June 21, 2019

初探WSL


What is WSL?

白話來說就是在Windows上執行Linux啦~ 但是比起一般的虛擬機器來說使用上會更方便,簡單,快速。畢竟這是Windows自己就打算支持的功能嘛。

WSL是微軟與Canonical合作開發並於2016年正式發表,它運作的原理就是在Windows系統裡擔任上層Linux application與Windows NT kernel之間翻譯的橋樑,看下圖不難理解吧?


What can WSL do?

WSL除了可以像虛擬機器讓使用者在Windows上使用Linux外,它主要的賣點應該是可以讓Windows與Linux無縫整合在一起,也就是說在Windows cmd下可以使用Linux的命令,比如:find, awk, sed, grep ....., etc,如果有需要還可以透過package management(apt or yum) 去安裝需要的軟體,更好玩的是你可以在Windows上面運行X window,讓WSL執行運算,然後Windows負責顯示。

Requirements

1. 安裝64 bit的Windows10 (Windows 2019似乎也支援)

2. 版本等於或大於1607


Installing WSL

4個步驟即可安裝跟配置好!
1. Open a new PowerShell as Administrator.

2. At the PowerShell prompt, run the following command:
Enable-WindowsOptionalFeature -Online -FeatureName Microsoft-Windows-Subsystem-Linux

3. Reboot Windows.

4. To install Linux distros from Windows Store.


Demonstrate - Getting started Ubuntu 

安裝完後,不用懷疑直接點選Ubuntu的icon就可以運行Linux。


Demonstrate - execute Linux tools 

之前說到在Windows下無縫接軌使用Linux command的方法有三種:
1. wsl [Linux command]

2. bash -c “Linux command”

3. ubuntu1804 run [Linux command]


上面這個例子就是在Windows cmd下使用Linux的ifconfig, grep, awk去過濾出系統的IPv4 addresses.


Demonstrate - X window

簡單三步驟讓你的Windows搖身一變成X window.
1. 下載Xming for Windows10.

2. 開啟Ubuntu並透過apt安裝常用的desktop applications.
$ sudo apt install ubuntu-desktop

3. 在Ubuntu裡把X window display設定成本機127.0.0.1:0
$ export DISPLAY=127.0.0.1:0


以上可以看到我可以在Windows底下透過Ubuntu使用xeyes, Firefox, Thunderbird, GIMP。


WSL2 is coming
剛剛所介紹的都是WLS1,微軟近期將打算推出WLS2並且號稱比WSL1會有更好的效能改進,主要的原因是它真的在Windows上運行Linux kernel! 而且第一個版本的kernel會是4.19!

WSL2可以說是整個架構的翻新( 參考下圖),它不在只是擔任翻譯的角色而是真正的Linux kernel,可以預期有更好的支援性,比如你將有機會在Windows下透過WLS2執行snap, docker, Kubernetes等等。

將來還可以透過Windows update來更新Linux kernel,微軟真的從此愛上了Linux嗎?讓我們繼續看下去~

參考:

Tuesday, June 11, 2019

如何在Ubuntu 18.04定期做資料備份到Google drive

上星期放連假,看到了一篇文章介紹如何在Ubuntu 18.04下透過內建的backup軟體將本機資料定期備份到Google drive,有興趣的朋友可以參考以下的連結來實做看看:
https://vitux.com/how-to-schedule-file-backups-to-google-drive-on-ubuntu/
主要的步驟就是先在Ubuntu Online Accounts註冊好你的Google account。(Google預設有免費15GB的使用空間),並且記得Files一定要選到。


接著打開Nautilus window,你應該會看到你的Google account會出現在側邊欄,請記得點選它。(感覺如同去mount一個USB或外接硬碟之類的)


這時候系統應該可以成功存取Google drive,然後參考上邊的連結去設定Ubuntu backup tool。

如果將來需要restore資料的話,一樣可透過Ubuntu backup tool執行restore的動作。

Step1. 點選Restore button.


Step2. 從Google drive來restore.


Step3. 從哪一天的資料restore.


Step4. 選擇要restore到本機哪個資料夾。


Wednesday, May 29, 2019

測試網路下載速度的小工具

在Ubuntu下若想要簡單測試目前Internet下載速度的話,可以用Netflix出的一個小軟體fast來測試。

安裝:
$ snap install fast

執行
$ fast


就是這麼簡單。

Monday, May 13, 2019

Canonical QA offsite meeting之Python 練習

5月初部門舉辦了一次offsite meeting,主題是學習Python。

內部同事兼講師,教材準備得很好,上課內容又豐富,所以當然要把回家作業完成。

Exercise 1

Write a function that takes a string and returns the inverted string (e.g. Taiwan → nawiaT). This function must use a for loop.

Exercise 2

Same as exercise 1, but using the easiest/shortest way (hint: the answer is somewhere in the previous sections.

Exercise 3

Dictionary containing all Ubuntu releases. The key is the release number (e.g. “18.04”) and the value is the release codename (e.g. “Bionic Beaver”):

  • Using Python code:return the release codenames for versions released in October
  • find how many releases were released neither in April nor October
  • return the version number for versions whose codename contains a “k”

Exercise 4

Write a function that reads the content of a text file and returns a dictionary with the number of occurrences for each letter of the alphabet

以下是我寫的code:

Exercise 1

def revert(word):
    for i in range(len(word)-1, -1, -1):
        print(word[i],end="")

revert("I love Taiwan")

Exercise 2

string="Taiwan"
print(string[::-1])

Exercise 3

Ubuntu={ "4.10": "Warty Warthog", "5.04": "Hoary Hedgehog", "5.10": "Breezy Badger", "6.06": "Dapper Drake", "6.10": "Edgy Eft", "7.04": "Feisty Fawn", "7.10": "Gutsy Gibbon", "8.04": "Hardy Heron", "8.10": "Intrepid Ibex", "9.04": "Jaunty Jackalope", "9.10": "Karmic Koala", "10.04": "Lucid Lynx", "10.10": "Maverick Meerkat", "11.04": "Natty Narwhal", "11.10": "Oneiric Ocelot", "12.04": "Precise Pangolin", "12.10": "Quantal Quetzal", "13.04": "Raring Ringtail", "13.10": "Saucy Salamander", "14.04": "Trusty Tahr", "14.10": "Utopic Unicorn", "15.04": "Vivid Vervet", "15.10": "Wily Werewolf", "16.04": "Xenial Xerus", "16.10": "Yakkety Yak", "17.04": "Zesty Zapus", "17.10": "Artful Aardvark", "18.04": "Bionic Beaver", "18.10": "Cosmic Cuttlefish", "19.04": "Disco Dingo" } for number in Ubuntu.keys(): if number.split(".")[1]=="10": print("OCT=",Ubuntu[number]) for number in Ubuntu.keys(): if number.split(".")[1]!="10" and number.split(".")[1]!="04": print("Neither in APR or OCT:",Ubuntu[number]) for codename in Ubuntu.values(): if "k" in codename.lower(): print("Codename contains a K or k:",codename)

Exercise 4

LIST=[]
for w in range(ord('a'), ord('z') + 1):
    LIST.append(chr(w))

ACCOUNT=[]
for i in range(0,26):
    ACCOUNT.append(0)

with open('/usr/share/doc/python3/copyright','r') as f:
    for alphabet in f.read():
        for i in range(0,26):
            if alphabet.lower()==LIST[i]:
                ACCOUNT[i]=ACCOUNT[i]+1
                break


dictionary=dict(zip(LIST,ACCOUNT))
print(dictionary)

老實說我有一段時間沒寫程式了,但稍微學習了一下Python後,它的語法很簡潔好懂,果然是受歡迎的程式語言之一呀!

Wednesday, May 08, 2019

在Ubuntu 18.04 Server 快速架設FreeRADIUS Server

比起以前在Linux架設FreeRADIUS server的難度與花費的時間,目前在Ubuntu安裝並配置FreeRADIUS server真的是輕鬆了許多。廢話不多說,以下筆記如何在Ubuntu Server 18.04安裝並且配置一台可以使用的FreeRADIUS server。

環境:
Ubuntu Server 18.04.02 LTS


安裝:
# apt install freeradius


配置:
1. 建立使用者帳號:
先切換到FreeRADIUS server的目錄,然後開啟檔案users。
# cd /etc/freeradius/3.0
# vi users


這裡我將套用一個內建的帳號bob:


修改clients.conf: (這個檔案主要是限制哪些client可以使用FreeRADIUS server)
# vi clients.conf


以上我新增了於subnet 10.101.47.0/24的client都可以使用FreeRADIUS server,並且secret是testing123。

重新啟動FreeRADIUS server:
# systemctl restart freeradius
# systemctl status freeradius


從遠端機器驗證:
$ radtest bob hello 10.101.47.37 1812 testing123

bob -> 帳號
hello -> 密碼
10.101.47.37 -> FreeRADIUS server's IP
1812 -> FreeRADIUS server's port (認証用)
testing123 -> FreeRADIUS server's secret


一個FreeRADIUS server到這邊已經可以正常運行在Ubuntu Server 18.04,有空在跟大家介紹如何讓FreeRADIUS支援802.1X或是結合mysql儲存使用者的帳號密碼。

Friday, April 12, 2019

移除一些舊版的snap packages來增加disk space

找到一篇不錯的文章,可以幫助user去移除一些也許已經用不到的舊版snap packages,這點對我來說蠻實用的,因為我的系統透過snap裝了蠻多軟體,而且預設上snap會針對每個軟體同時存著三個版本(如果有軟體本身有升級過好幾次),好處是萬一將來發現升級上來的軟體有bug,之後可以馬上revert package,但缺點就是比較浪費硬碟空間。(你可以想像系統同時間裝了三份相同的軟體)


比較一下執行script前與後的使用空間:
Before:


After:


真的差蠻多的~ 萬一系統空間不足時,建議可以先清理一下snap舊版的軟體。

Wednesday, April 03, 2019

解決Virtualbox無法在Secure boot下使用的問題

其實我的X1 Carbon 6th在Ubuntu 18.04遇到這個問題有些日子了,但總覺得沒有必需立馬解決它。

這個現象的主要原因是Virtualbox的dkms並不是預設Secure boot認得的firmware,所以當你想要運行Virtualbox時會碰到這個問題,kernel會一直無法掛載vboxdrv。


解決的方法有兩種:

  • 回到BIOS/UEFI去關閉Secure boot。
  • 讓Secure boot保持運行,然後手動去註冊Virtualbox相關的kernel module。

這裡我選擇讓Secure boot保持運行並且產生MOK(Machine Owner Key)keys註冊到Secure boot,以下就來實作吧!

Steps:

  • 建立signing keys:

openssl req -new -x509 -newkey rsa:2048 -keyout MOK.priv -outform DER -out MOK.der -nodes -days 36500 -subj "/CN=Descriptive name/"

  • 註冊Virtualbox相關的modules:


sudo /usr/src/linux-headers-$(uname -r)/scripts/sign-file sha256 ./MOK.priv ./MOK.der $(modinfo -n vboxdrv) 
sudo /usr/src/linux-headers-$(uname -r)/scripts/sign-file sha256 ./MOK.priv ./MOK.der $(modinfo -n vboxnetflt)


  • 註冊keys到Secure boot:

sudo mokutil --import MOK.der
這個時候系統會要求你輸入一組密碼,先記起來等一下跑Enroll MOK utility時會用到。
  • Reboot system+運行MOK:
Enroll MOK -> Continue -> Yes -> Input password -> Reboot system again
這邊有個例子提供上述步驟的screenshots可以參考https://sourceware.org/systemtap/wiki/SecureBoot

  • 重新掛載vboxdrv與vboxnetflt: 

sudo modprobe vboxdrv
sudo modprobe vboxnetflt

  • 啟動Virtualbox


成功了!現在系統可以跑Virtualbox了。

Thursday, March 07, 2019

如何解決Lenovo X1 Carbon 6th 在Linux下無法休眠(S3)的問題?

是的這個問題困擾了我一陣子,今天上網搜尋了一下總算是找到了解決的方法。

首先確定把BIOS升級到1.30以上。(可以透過dmidecode查看)


接下來,將系統重新開機後進入BIOS去選擇: (Default設定是Win10)
Config -> Power -> Sleep State -> Set to Linux

到這邊已經完成了,系統測試一切正常!
Operating System: Ubuntu 18.04.2 LTS
Kernel: Linux 4.15.0-46-generic
Architecture: x86-64

Ubuntu 16.04.6 LTS 釋出囉!

Canonical最近釋出了Ubuntu 16.04.6 LTS更新版本,這一次的更新主要是針對修正APT相關的安全性問題(CVE-2019-3462)。

ISO檔案可以透過以下連結來下載:
http://releases.ubuntu.com/xenial/

另外APT的漏洞在14.04, 18.04, 18.10也都存在相同的問題,不過不用太擔心!只要透過一般的軟體更新機制就可以修正APT安全性的問題。


Friday, February 22, 2019

如何在Ubuntu 18.04.2建立一個anonymous FTP server?

FTP算是一個非常古老的檔案傳輸通訊協定,雖然現今已經不像以前那樣舉足輕重了,但是偶爾拿來使用一下還是挺方便的。

稍微紀錄一下如何在Ubuntu 18.04.2 Desktop建立一台anonymous FTP server。

安裝:
$ sudo apt update && apt install vsftpd

Ubuntu現在很好玩,當你安裝好任何一個service的時候,systemd就會自動把它enable與active,你可以透過以下的命令快速驗證一下:
$ systemctl status vsftpd
$ netstat -tupln | grep ftp


修改vsftpd.conf:
預設vsftpd並不允許anonymous去做檔案的上傳或下載,所以我們需要改變幾個參數讓它支援。
$ sudo vi /etc/vsftpd.conf
# Allow anonymous FTP? (Disabled by default).
anonymous_enable=YES

# Uncomment this to enable any form of FTP write command.
write_enable=YES

# Uncomment this to allow the anonymous FTP user to upload files. This only
# has an effect if the above global write enable is activated. Also, you will
# obviously need to create a directory writable by the FTP user.
anon_upload_enable=YES

改完之後記得重啟
$ sudo systemctl restart vsftpd

建立anonymous FTP folder:
Ubuntu預設的FTP server folder是在/srv/ftp,所以欲分享的檔案可以放在這邊。下圖你可以看到我share的檔案(左)可以被遠端的FTP client抓取(右)。


接下來建立一個folder pub under /srv/ftp來讓遠端user可以透過FTP上傳檔案。
$ cd /srv/ftp
$ sudo mkdir pub
$ sudo chmod 777 pub
$ sudo chown ftp.ftp pub


以上一個anonymous FTP server已經可以開始對外提供服務了,當然之後可以更進一步地研究如何架設一個regular user從自己的家目錄上傳或下載檔案。

補充:
如果你有開ufw(UncomplicatedFirewall)而且預設針對incoming traffic都是deny的話,記得加一下允許FTP連線的rule,例如:
$ sudo ufw allow from any to any port 20,21 proto tcp
(這邊暫時不考慮FTP PASV mode, 所以只需要開放TCP port 20,21) 

如何在Ubuntu 18.04 LTS開啟HWE(Hardware Enablement Stack)

簡單的說明一下我個人覺得HWE的主要用途:


透過HWE為現有的Ubuntu LTS版本(Desktop, Server, Cloud)提供了更新的Kernel和X來進一步支援新的硬體。比方說預設18.04 LTS是採用Kernel 4.15,然而透過HWE的機制,使用者可以在18.04 LTS跑Kernel 4.18(18.10預設內核)。

以下透過Ubuntu Server來實做一下:

1. 檢查系統是否有支援HWE:
root@server1 ~# hwe-support-status --verbose


2. 開啟HWE:
root@server1 ~# sudo apt install --install-recommends linux-generic-hwe-18.04


3. 確定Kernel可以透過HWE更新到4.18:


是不是很簡單呢? :)

後記補充:
18.04.2 預設是安裝Kernel 4.18(Fresh install),但如果想從既有的18.04升級到18.04.2,看起來Kernel還是會停留在4.15,所以如果需要新的Kernel或是新的drivers,可以考慮透過HWE來升級這些部份。

Monday, February 11, 2019

Ubuntu 14.04 LTS即將步入End of Life

還在使用Ubuntu 14.04 LTS的發行版本嗎? 但是14.04即將在2019/4/30步入End of Life囉~ 所以到時候就沒有辦法繼續讓14.04 LTS的機器可以享有最新版本的Linux Kernel或是應用軟體安全性相關的升級.

不過其實也不用太擔心啦! 一般用戶的話, 建議可以把14.04考慮升級成16.04或是18.04 LTS, 但如果是企業用戶還想停留在14.04操作環境的話其實可以考慮Canonical Ubuntu Advantage讓運行在企業裡面的Ubuntu 14.04 LTS將來持續有安全性更新.

至於如何將14.04升級到16.04或是18.04呢? 其實步驟很簡單, 可以參考以下的連結透過全圖形化介面就可以輕鬆升級:
https://tutorials.ubuntu.com/tutorial/tutorial-upgrading-ubuntu-desktop#0

順帶一提2019/3/6有個線上的session可以參考囉~
How to ensure the ongoing security compliance of Ubuntu 14.04 LTS ‘Trusty Tahr’

Saturday, February 02, 2019

ThinkPad X1 Carbon 6th + Ubuntu 18.04 + LVFS

前言:

以往Linux的使用者如果要做BIOS或韌體升級的話,通常實作的方法有兩種:

1. 切換到Windows去執行廠商所提供的工具來升級。
2. 手動抓取相關的firmware然後自行製作開機disk來升級。
換句話說,其實對Linux使用者是挺不方便的,所以有人提出了LVFS project這個好主意。

LVFS(Linux Vendor Firmware Service)? 其實白話來說就是提供一個public pool然後邀請各家OEM/ODM廠商把自家最新的硬體firmware放上去,之後Linux系統便可以會透過fwupd這隻daemon去下載並且更新最新的firmware。

更多詳細的資訊可以參考LVFS的網站:
https://fwupd.org/users

以下是我擷取Ubunut 18.04在GNOME的畫面,可以看到我的X1有相關新firmware或是BIOS可以更新了。


所以如果Linux系統提醒你/妳可以升級BIOS的時候,也不用太訝異囉~ :D

Tuesday, January 08, 2019

Canonical Livepatch service

其實我沒接觸過Canonical Livepatch service,直到公司內部有同事在internal meeting裡面介紹後,我才發現到這個功能對於廣大的IT人員將會是一個非常好用的功能,而且某些程度上還可以減少些出錯的機會。

關於Canonical Livepatch service,我個人覺得它最主要的目的就是可以讓Linux kernel安裝上一些fixes但是系統不需要重新開機!而且kernel也不需要整個升級,相信對於一些系統必需保持在某個版本的kernel,或是不允許重新開機跟system downtime很要求的環境,這個功能確實是非常實用!

Canonical livepatch service其實在Ubuntu 14.04就開始支援了,但當時只支援CLI去配置Canonical livepatch service,不過從18.04之後,在GUI就可以很簡單的開啟以及使用它。

關於CLI如何使用,可以參考以下的連結:
https://blog.ubuntu.com/2017/06/06/canonical-kernel-livepatch-service-now-available-for-ubuntu-14-04-lts
https://www.ubuntu.com/livepatch 

GUI的話可以參考下面幾個步驟:
1. Software & Updates -> Updates.


2. 點選Sign in button.


3. 輸入你的Ubuntu SSO帳號(Ubuntu One account)。


4. 接著輸入Ubuntu 2 factor authentication。


如果順利的話,你可以看到Sing in button變成Sing Out,順便用CLI檢查一下。


所以當Sing in成功後,系統會從snap store自動安裝canonical-livepatch,相關的token也會自動抓取下來,比起14.04 or 16.04來說真的方便許多!

最後這邊要注意一下,Canonical livepatch service預設一組Ubuntu One帳號只允許3台機器使用,如果你是企業用戶的話,那可以考慮Ubuntu advantage來支援更多的機器。

Thursday, January 03, 2019

在Ubuntu 18.04 架設VNC Server

很久前有筆記過如何在CentOS7上架設VNC Server,這幾天實做了一下VNC Server在Ubuntu 18.04上。

以下就簡單紀錄一下步驟。

Steps:
1. Install VNC Server (遠端桌面環境將採用xfce):
$ sudo apt-get install vnc4server xfce4 xfce4-goodies
2. 建立VNC server的配置檔與user密碼:
$ vncpasswd
$ vim.tiny ~/.vnc/xstartup
#!/bin/sh
unset SESSION_MANAGER
unset DBUS_SESSION_BUS_ADDRESS
exec startxfce4 
$ chmod 755 ~/.vnc/xstartup
3. 手動啟動VNC Server:
這個時候我們先測試看看VNC Server可不可以正常工作。


如果有看到以上類似的畫面,那說明VNC Server已經啟動並且listen在TCP port 5901。但是請注意,預設它會只listen在localhost,這個等一下在建立systemd startup script的時候,我們可以修改它。
4. 建立systemd startup script: 
 做這個設定的最大好處是將來系統重開機後,我就不需要每次都要手動啟動VNC Server了。
4.1 建立VNC Server script file:
 $ sudo vim.tiny /etc/systemd/system/vncserver@.service
[Unit]
Description=Remote desktop service (VNC)
After=syslog.target network.target

[Service]
Type=simple
User=u
PAMName=login
PIDFile=/home/%u/.vnc/%H%i.pid
ExecStartPre=/bin/sh -c '/usr/bin/vncserver -localhost no -kill :%i > /dev/null 2>&1 || :'
ExecStart=/usr/bin/vncserver :%i -localhost no -geometry 1440x900 -alwaysshared -fg
ExecStop=/usr/bin/vncserver -kill :%i

[Install]
WantedBy=multi-user.target
剛剛有提到預設VNC Server只會listen在localhost:5901,但透過參數-localhost no可以讓它listen在0.0.0.0也就是all net的概念。 
4.2 手動reload systemd: (每次有新增或修改systemd的startup script file後,記得此步驟)
$ sudo systemctl daemon-reload
4.3 透過systemd啟動VNC Server:
$ sudo systemctl start vncserver@1.service
4.4 在系統開機時,自動啟動VNC Server:
$ sudo systemctl enable vncserver@1.service
假設一切順利的話,輸入相關的命令後,應該可以看到類似的畫面。


 5. 遠端測試: (採用Ubuntu內建的Remmina remote desktop client)

Friday, December 28, 2018

2018 Top 10的Snap 套件

即將邁入2019,回顧一下2018 前10名最受喜愛的snap套件是哪些呢?

剛看了一下敝公司的官方網頁,以下有Top10的排行榜唷~ :D
https://blog.ubuntu.com/2018/12/27/top-snaps-in-2018

不過說真的,我個人蠻常用的Skype, mailspring, simplenote現在都用snap來安裝,並且會自動定時更新,超方便的呀~

不知道何時會有line for snap?

Wednesday, September 19, 2018

How can I setup an IPv6 router via radvd on Ubuntu 18.04 LTS?

What's radvd?
Router advertisement daemon.

Reference:
https://zh.wikipedia.org/wiki/Radvd
http://www.litech.org/radvd/

一般來說 IPv6 Client決定Global IPv6的方式有兩種,分別是Stateless與Stateful,預設radvd是採用stateless IPv6,不過透過更改某個參數(M flag),就可以轉換成stateful,但是此時網路上必須有對應的DHCPv6 server來負責管理與分配IPv6 address。

網路上可以找到很多先進寫的資料關於Stateless與Stateful的差異,我也就不班門弄斧了,廢話不多說,直接進入主題,如何架設radvd在Canonical/Ubuntu 18.04 LTS。

Steps:

Step1. Install radvd package.
$ sudo apt-get install radvd
Step2. Copy example file of radvid.conf from /usr/share/doc/radvd/examples/ to /etc.
$ sudo cp /usr/share/doc/radvd/examples/radvd.conf.example /etc/radvd.conf
Step3. Open/Edit radvd.conf
根據你的需求,去配置相關的參數,最重要的應該是prefix,更多詳細的參數可以參考man page。
https://www.systutorials.com/docs/linux/man/5-radvd.conf/
Step4. Restart radvd
$ sudo systemctl restart radvd; sudo systemctl enable radvd

以上一個簡單的IPv6 stateless的Router已經架設完成,IPv6 client現在自己可以搭配prefix自動產生host ID。


Wednesday, August 15, 2018

How can I configure Ubuntu 16 to start teamviewer automatically?

Steps:

1. Opened /etc/init.d/rc.local

$ sudo vi /etc/init.d/rc.local


2. Added teamviewer's command and parameter below in file rc.local:
teamviewer passwd ubuntu
3. Restart system

4. Examine if teamviewer daemon can work as expected:

$ systemctl status teamviewerd
● teamviewerd.service - TeamViewer remote control daemon
   Loaded: loaded (/etc/systemd/system/teamviewerd.service; enabled; vendor preset: enabled)
   Active: active (running) since 三 2018-08-15 11:00:14 CST; 1min 25s ago
  Process: 1555 ExecStart=/opt/teamviewer/tv_bin/teamviewerd -d (code=exited, status=0/SUCCESS)
 Main PID: 1567 (teamviewerd)
   CGroup: /system.slice/teamviewerd.service
           └─1567 /opt/teamviewer/tv_bin/teamviewerd -d

$ ps aux | grep -i teamviewer
root      1567  0.3  0.3 1181612 12212 ?       Sl   11:00   0:00 /opt/teamviewer/tv_bin/teamviewerd -d
u         1890  0.3  2.2 1990224 88556 ?       Sl   11:00   0:00 /opt/teamviewer/tv_bin/TeamViewer

Afterwards, you can remote control host via Partner ID and password which is ubuntu in this example.


Friday, May 04, 2018

How can I create a multiboot USB stick from Linux?

You can refer to https://www.pendrivelinux.com/multiboot-create-a-multiboot-usb-from-linux/

It works for me!


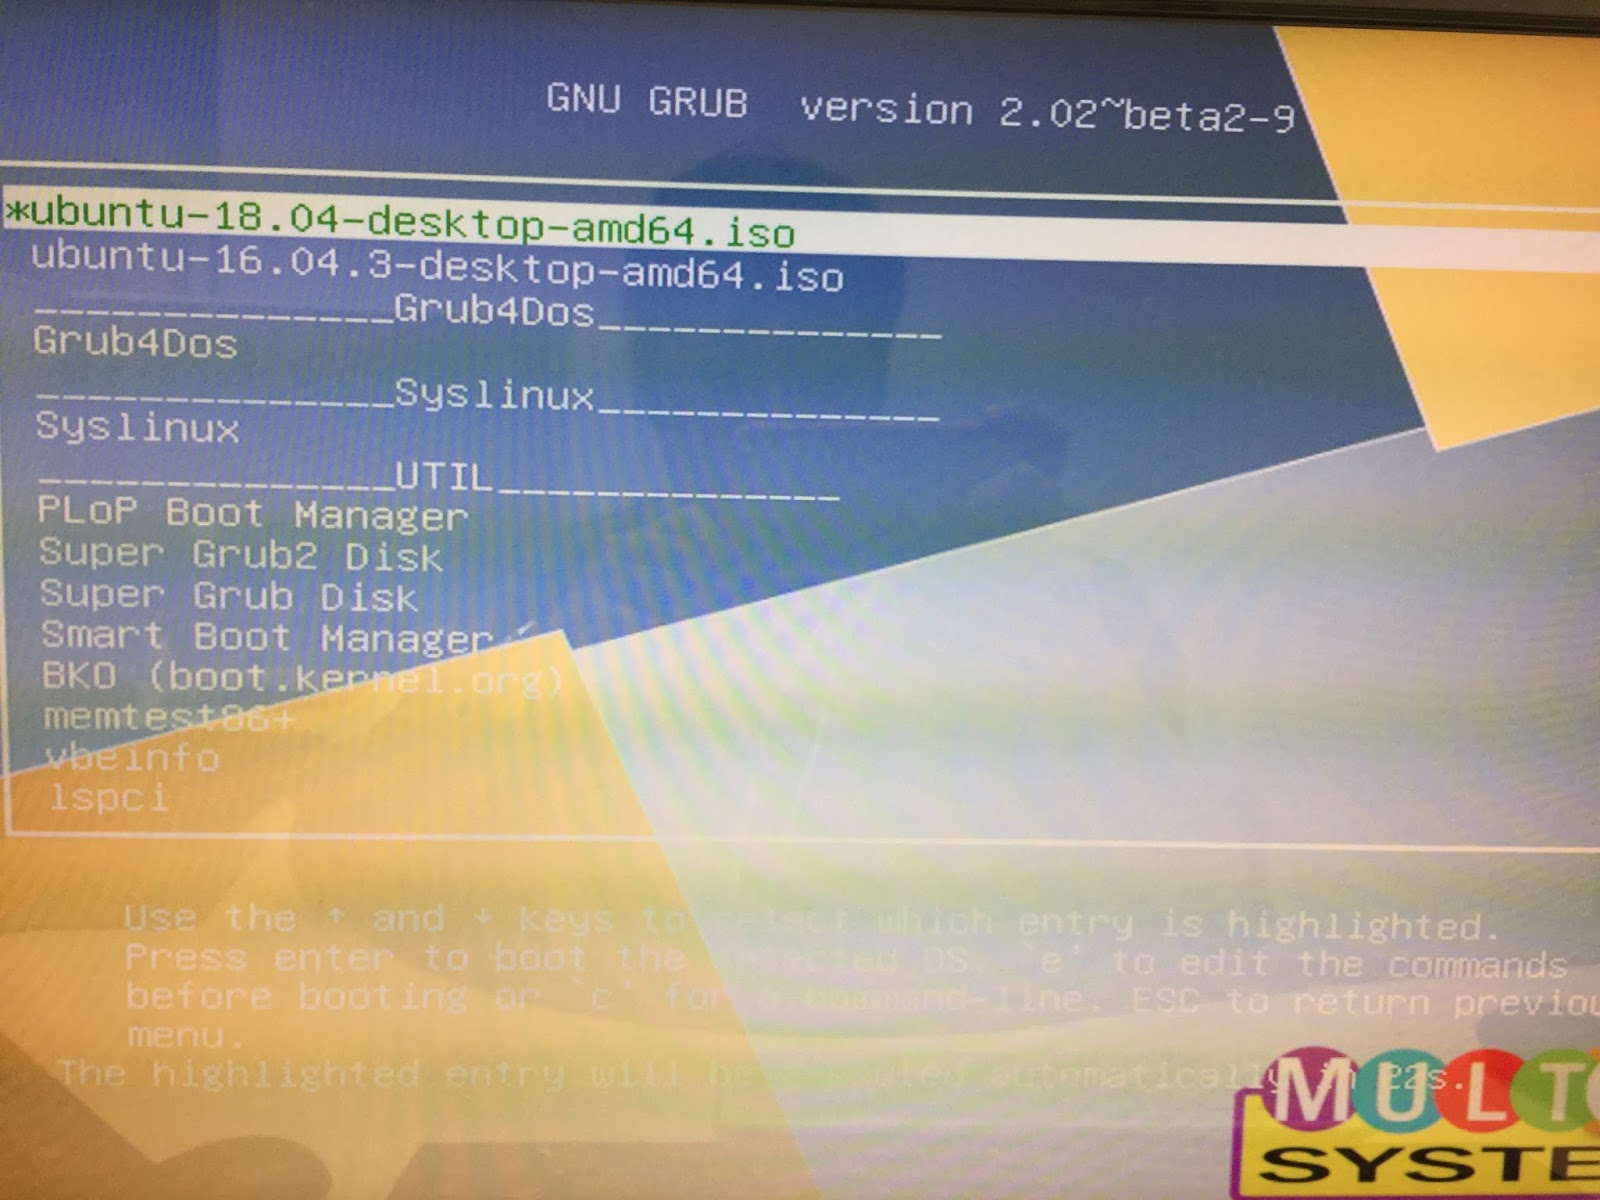
Above you can see that I am able to boot Ubuntu 16.03 as well as 18.04 with one USB stick w/o problem.

But somehow you've to disable security boot in BIOS.

Enjoy~

How can I setup a proxy server in Ubuntu 16.04?

Step1. Install package squid
# sudo apt-get install -y squid

Step2. To setup common proxy settings:
# sudo vi /etc/squid/squid.conf

To add some lines below:
# line 977
acl lan src 192.168.1.0/24
(where 192.168.1.0 means network you would like to allow client to access your proxy server)

# line 1189
http_access allow lan
(Allow lan here)

# line 1602
http_port 3128
(To modify default proxy port if needed)

Step3. Restart squid
# sudo systemctl restart squid

Step4. Examine squid service
# sudo systemctl status squid
● squid.service - LSB: Squid HTTP Proxy version 3.x
Loaded: loaded (/etc/init.d/squid; bad; vendor preset: enabled)
Active: active (running) since 四 2018-04-26 15:24:04 CST; 1min 56s ago
Docs: man:systemd-sysv-generator(8)
Process: 3088 ExecStop=/etc/init.d/squid stop (code=exited, status=0/SUCCESS)
Process: 3119 ExecStart=/etc/init.d/squid start (code=exited, status=0/SUCCESS)
CGroup: /system.slice/squid.service
├─3159 /usr/sbin/squid -YC -f /etc/squid/squid.conf
├─3161 (squid-1) -YC -f /etc/squid/squid.conf
├─3162 (logfile-daemon) /var/log/squid/access.log
└─3163 (pinger)

四 26 15:24:04 uc16-VirtualBox systemd[1]: Starting LSB: Squid HTTP Proxy version 3.x...
四 26 15:24:04 uc16-VirtualBox squid[3119]: * Starting Squid HTTP Proxy squid
四 26 15:24:04 uc16-VirtualBox squid[3159]: Squid Parent: will start 1 kids
四 26 15:24:04 uc16-VirtualBox squid[3119]: ...done.
四 26 15:24:04 uc16-VirtualBox systemd[1]: Started LSB: Squid HTTP Proxy version 3.x.
四 26 15:24:04 uc16-VirtualBox squid[3159]: Squid Parent: (squid-1) process 3161 started

# netstat -tupln | grep 3128
tcp6 0 0 :::3128 :::* LISTEN 3161/(squid-1)

Done ~

In proxy client side:
You can use tcpdump or wireshark to ensure that http request will go to proxy server after you configured http proxy server within browser.

root@server1:~$ sudo tcpdump -n -v -i any port 3128
tcpdump: listening on any, link-type LINUX_SLL (Linux cooked), capture size 262144 bytes
15:29:06.382845 IP (tos 0x0, ttl 64, id 2257, offset 0, flags [DF], proto TCP (6), length 145)
192.168.1.211.40994 > 192.168.1.254.3128: Flags [P.], cksum 0x85a5 (incorrect -> 0x9ba8), seq 670754847:670754940, ack 314235908, win 237, options [nop,nop,TS val 1731217504 ecr 1884649606], length 93
15:29:06.383195 IP (tos 0x0, ttl 64, id 35299, offset 0, flags [DF], proto TCP (6), length 212)
192.168.1.254.3128 > 192.168.1.211.40998: Flags [P.], cksum 0xbf6c (correct), seq 2355697405:2355697565, ack 1986317666, win 486, options [nop,nop,TS val 1884649610 ecr 1731217476], length 160
15:29:06.383264 IP (tos 0x0, ttl 64, id 17423, offset 0, flags [DF], proto TCP (6), length 52)
192.168.1.254.3128 > 192.168.1.211.40994: Flags [.], cksum 0xaba6 (correct), ack 93, win 503, options [nop,nop,TS val 1884649610 ecr 1731217501], length 0
15:29:06.383359 IP (tos 0x0, ttl 64, id 2258, offset 0, flags [DF], proto TCP (6), length 1353)
192.168.1.211.40994 > 192.168.1.254.3128: Flags [P.], cksum 0x8a5d (incorrect -> 0x8fe0), seq 93:1394, ack 1, win 237, options [nop,nop,TS val 1731217505 ecr 1884649610], length 1301
15:29:06.384198 IP (tos 0x0, ttl 64, id 9911, offset 0, flags [DF], proto TCP (6), length 268)